Offensive thinking. Engineering delivery. Controlled automation.
Secure what you build. Validate what you deploy.
ROO Secure IT Solutions helps engineering and security teams identify exploitable risk, harden cloud and delivery systems, and embed practical controls with human validation, explicit scope, and outcomes your teams can actually use.
Find exploitable risk before it reaches production.
ROO Secure IT Solutions combines offensive security thinking with practical DevSecOps and cloud engineering. We help organizations identify vulnerabilities, reduce attack surface, and build security into the way software and infrastructure are delivered.
Our approach is human-led and technology-assisted: automation and AI accelerate discovery, triage, and reporting while testing remains explicitly authorized, scoped, and auditable.
Tell us what you are building or deploying. We will help define a focused, authorized engagement — no generic playbooks.
Book a 30-minute scoping call →Security Engineering for Modern Organizations
Penetration Testing
Human-led testing for web applications, APIs, infrastructure, and cloud environments, supported by automation where it improves coverage.
DevSecOps Engineering
Security integrated into CI/CD with SAST, DAST, dependency, container, and infrastructure-as-code controls that teams can operate.
Cloud Security
Practical assessment and hardening for identity, workloads, network boundaries, configuration, containers, and cloud-native infrastructure.
Security Automation
Automated vulnerability workflows, telemetry analysis, remediation support, and repeatable security operations with human oversight.
Practical results from recent engagements
Teams typically see high-severity issues drop significantly within the first remediation cycle after prioritised testing and clear ownership.
Security gates (SAST, SCA, container, IaC) embedded into existing CI/CD without becoming a release bottleneck.
Authorised testing produces an evidence-based view of exposed assets, identity paths, and configuration risk.
Findings are manually confirmed and prioritised by exploitability and business impact, not raw scanner volume.
Security Built Into the Stack
Offensive Security & Vulnerability Management
Identify exploitable weaknesses across applications, infrastructure, APIs, and cloud environments, then turn findings into remediation priorities your teams can act on.
- Web application and API security testing
- Infrastructure and attack-surface assessment
- Vulnerability discovery, triage, and prioritization
- Security validation and remediation guidance
Multi-Cloud DevSecOps
Embed security controls into modern delivery pipelines and infrastructure without treating security as a final-stage review.
- AWS, Azure, GCP, and OCI environments
- Docker, Kubernetes, and Helm hardening
- Terraform and infrastructure-as-code security
- SAST, DAST, dependency, and container scanning
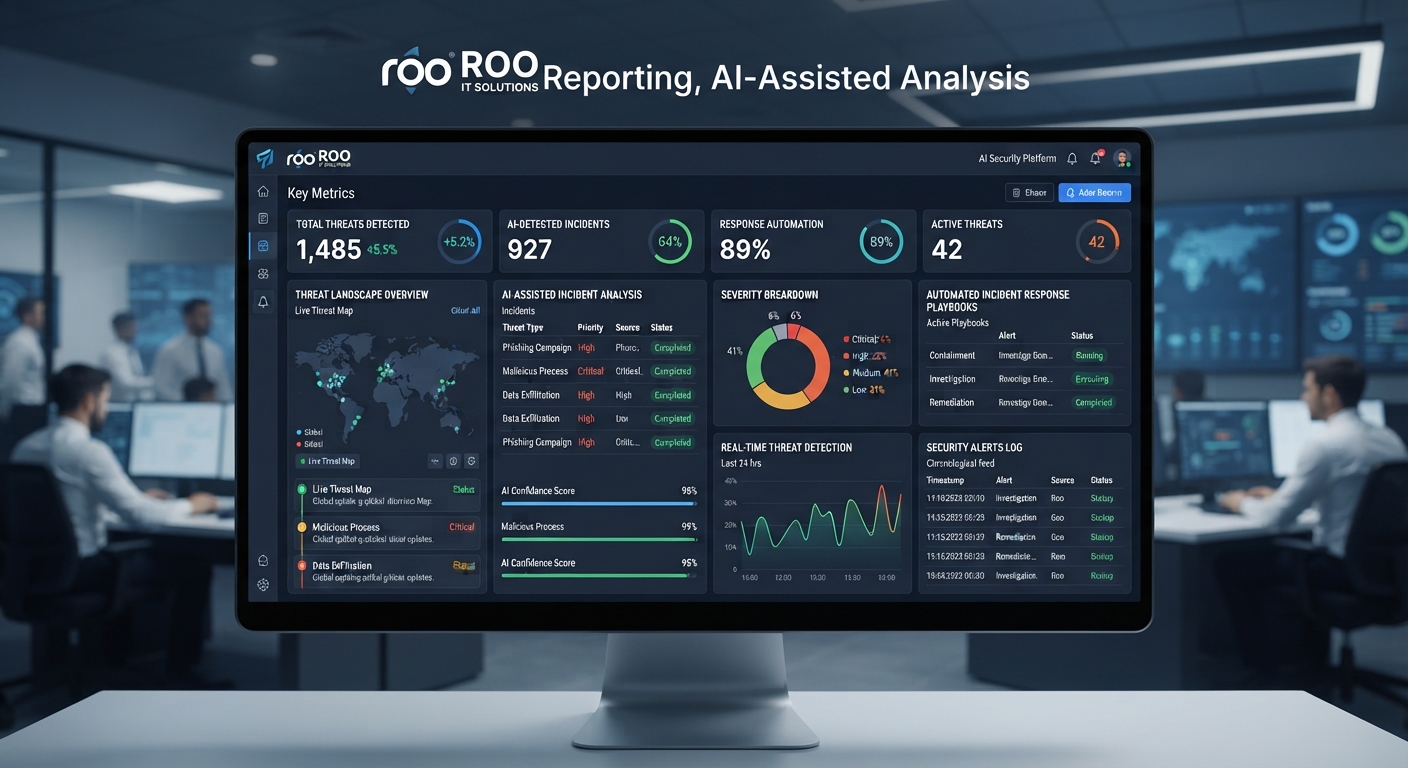
Security Automation & Controlled AI Assistance
Use automation and AI where they improve speed and analyst efficiency while keeping security decisions controlled, scoped, and auditable.
- Automated vulnerability triage and workflow orchestration
- Security log and telemetry analysis
- Threat-informed prioritization and reporting
- Human review and explicit scope for all security testing
Security Engineering in Practice
Representative client and technology engagements supported by ROO Secure IT Solutions. Detailed outcomes are shared under NDA during scoping.
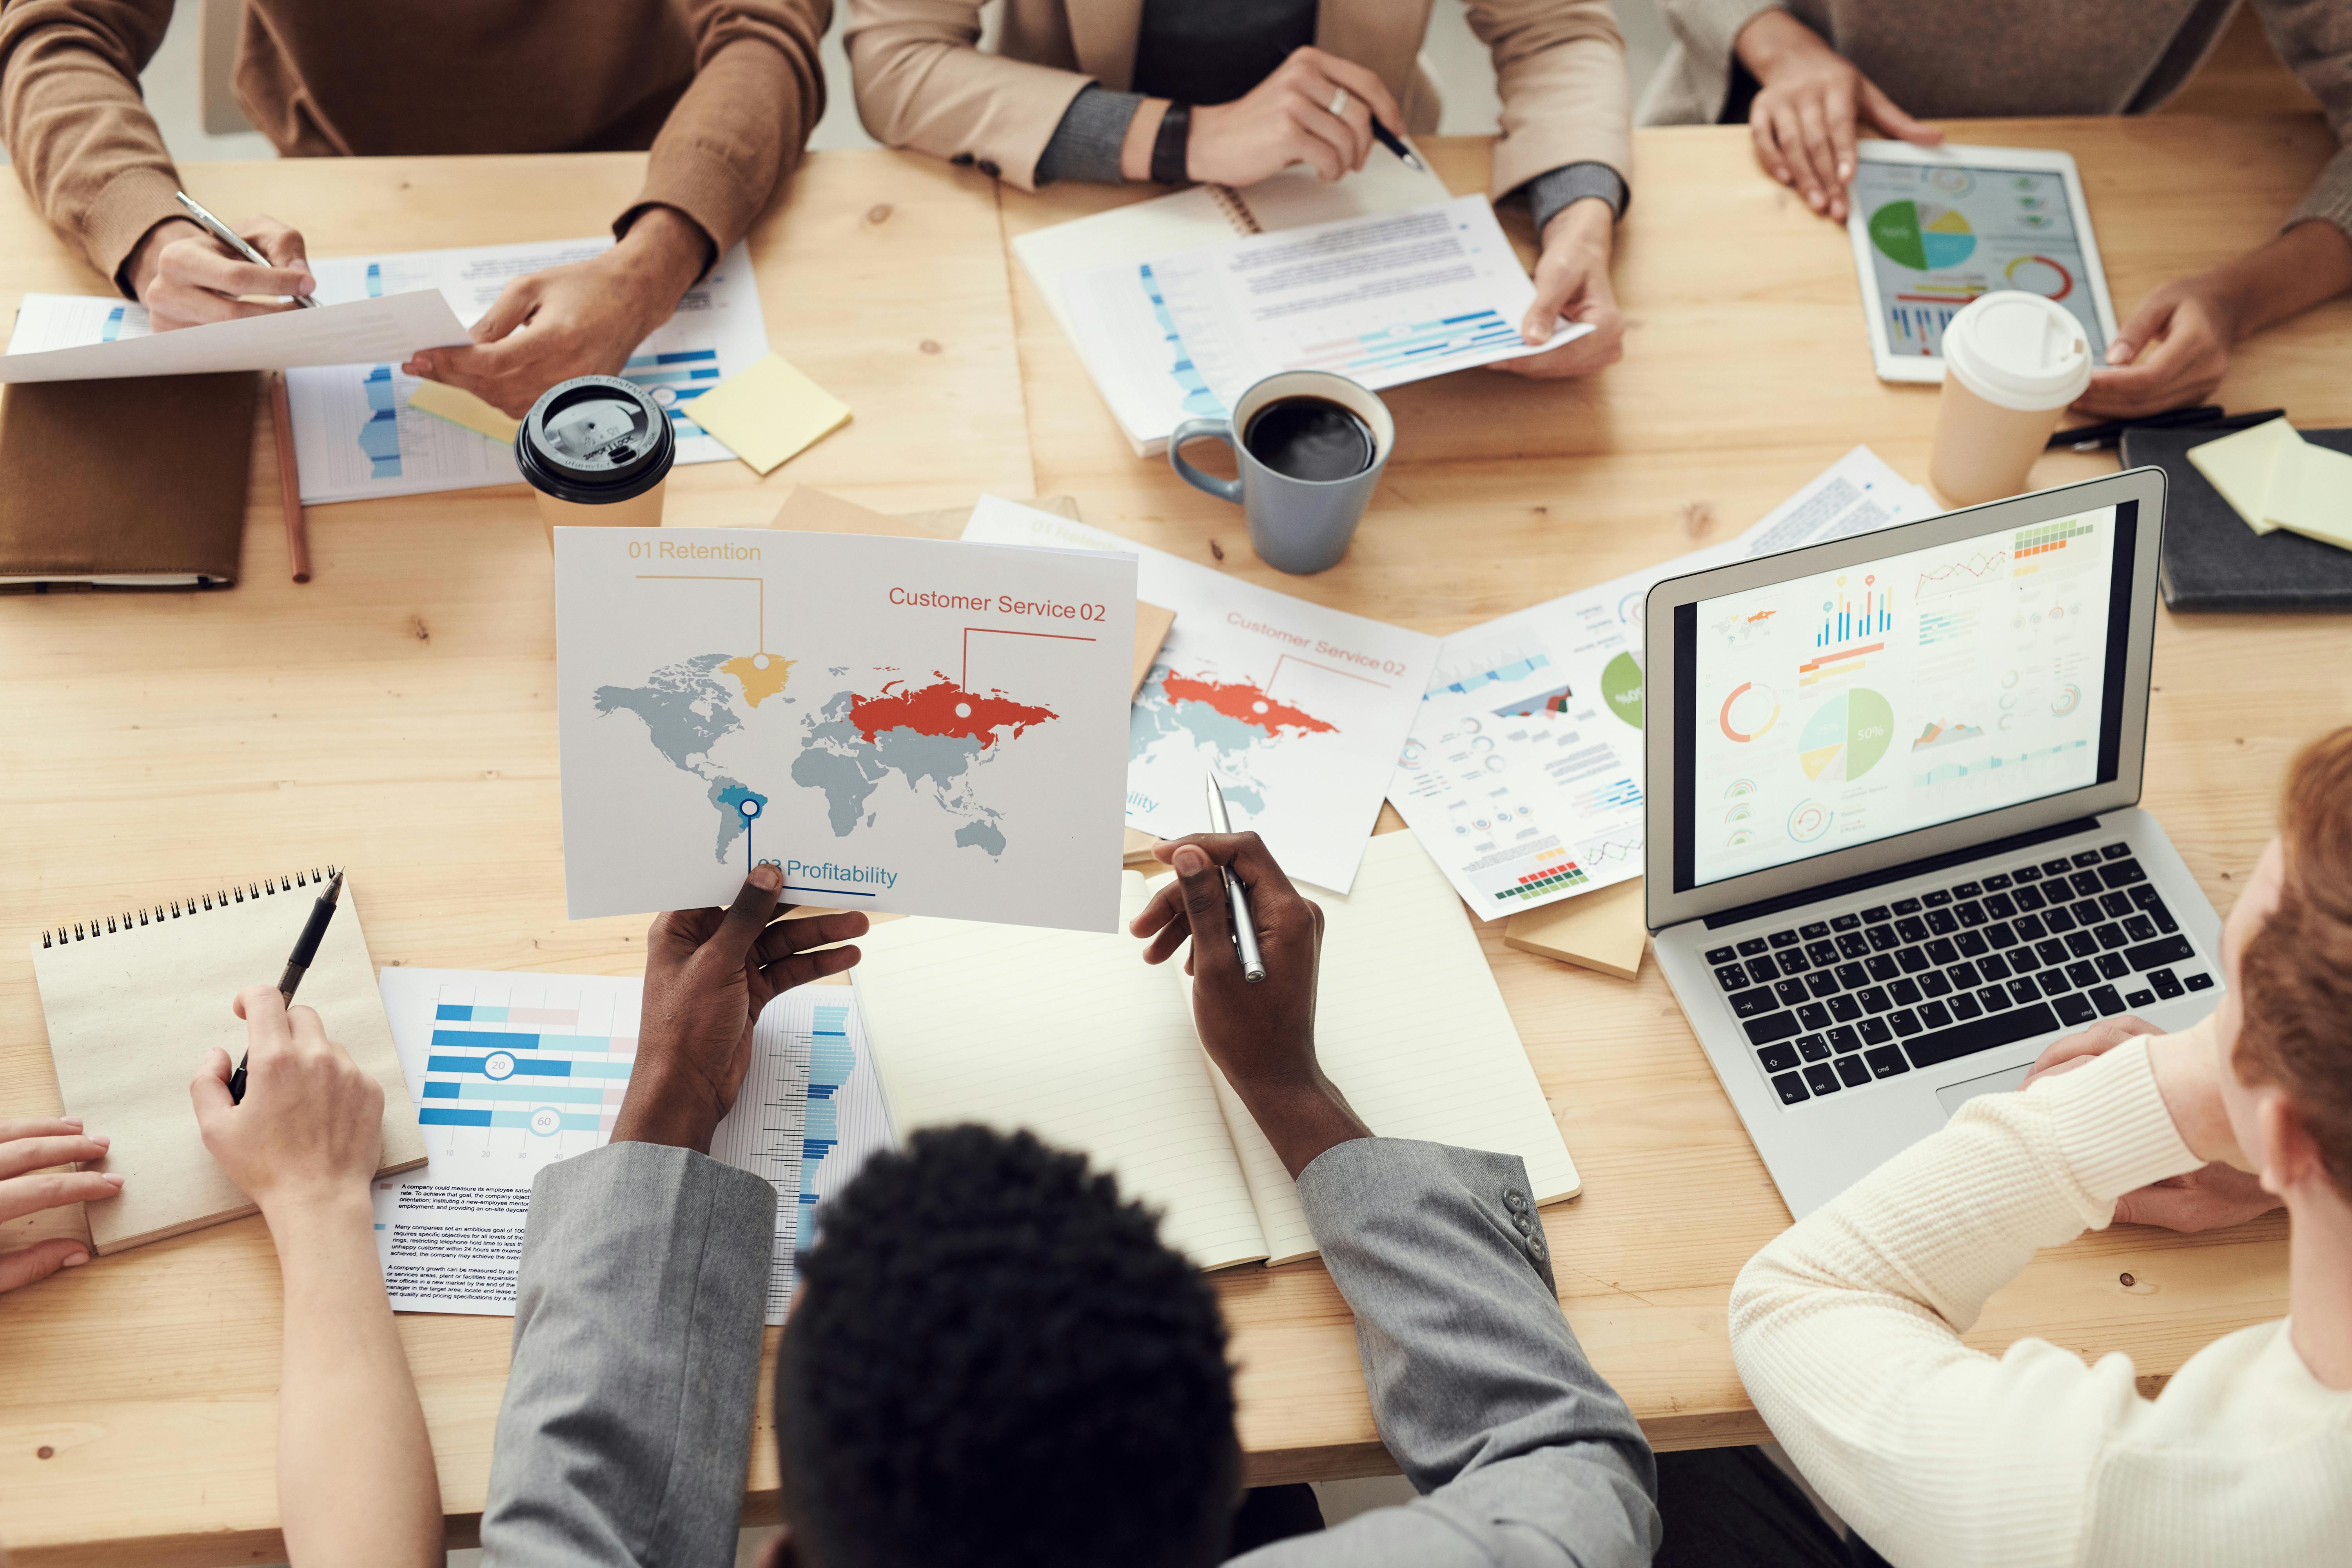
Security Monitoring & Automation
Visibility, monitoring workflows, and operational automation for continuous validation.
Secure Cloud Infrastructure
Cloud-native hardening, identity review, automation, and observability.
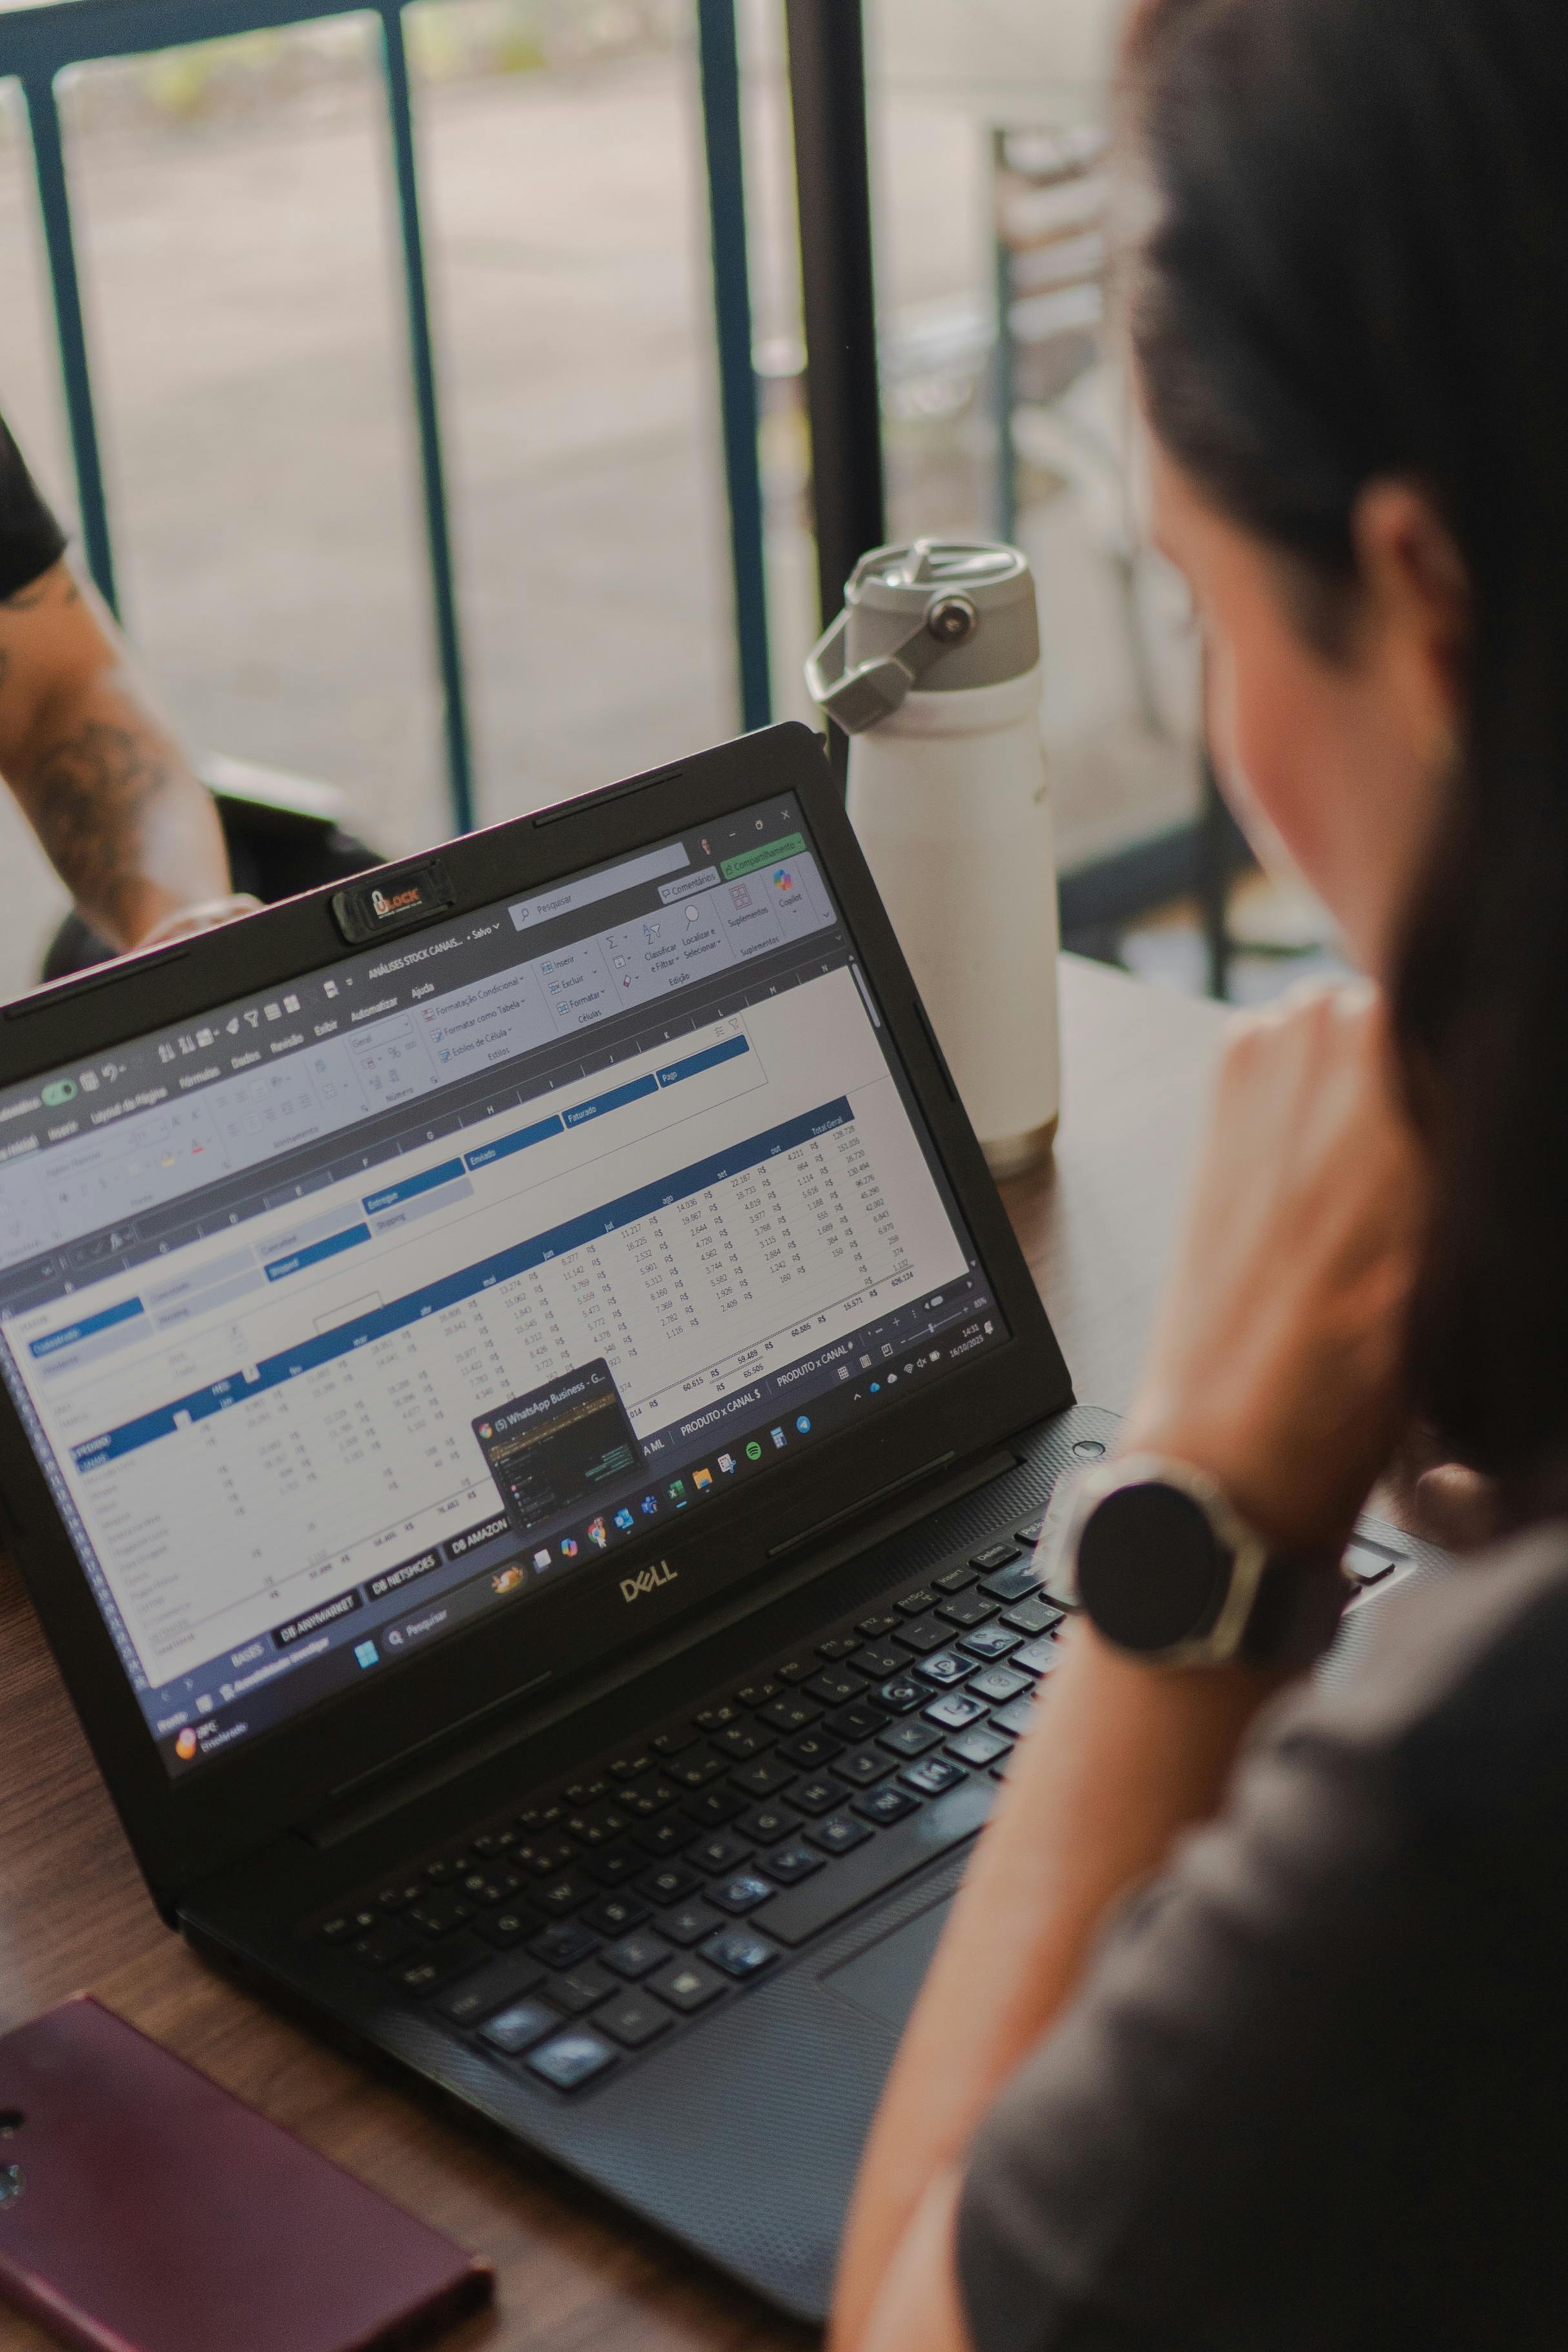
Security in the Delivery Pipeline
Controls integrated into application and infrastructure delivery without blocking velocity.
FAQ
How does ROO Secure IT Solutions approach penetration testing?
Engagements begin with explicit authorization and defined scope. Testing combines manual assessment and appropriate automation, followed by validation, prioritization, reporting, and remediation guidance. We do not run unscoped or unauthorised testing.
Can you integrate security into our existing CI/CD pipeline?
Yes. Security controls can be integrated into GitHub Actions, GitLab CI, Jenkins, and Azure DevOps workflows, including SAST, DAST, dependency, container, and infrastructure-as-code checks.
What environments can you assess?
Services can be scoped around web applications, APIs, infrastructure, containers, Kubernetes environments, and cloud platforms including AWS, Azure, GCP, and OCI.
How do you use AI in security engagements?
AI can assist with analysis, triage, log interpretation, workflow automation, and reporting. Security testing remains explicitly scoped and subject to human validation at every decision point that affects risk.
Can an assessment be customized to our environment?
Yes. Engagements are scoped around your applications, infrastructure, business objectives, technology stack, and risk priorities — never a one-size-fits-all checklist.
Know your attack surface before attackers do.
Tell us what you are building, deploying, or trying to secure. We will help define the right authorised engagement for your environment.
Selected organisations across healthcare, media, and technology. Detailed references available under NDA.

Get Started with ROO Secure IT Solutions
Tell us about your security needs. We will help define the appropriate next step — usually a short scoping conversation.